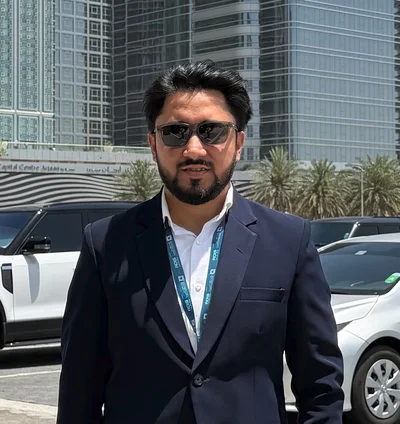
Cloud DevOps & Infrastructure Engineer.
3+ years engineering enterprise network backbones and production cloud infrastructure—transitioning from routing/switching (CCNP/CCNA, BGP/OSPF, SD-WAN) to declarative Kubernetes, Terraform IaC, and GitOps architectures.
Specializing in high-reliability AWS/Azure platforms, zero-drift CI/CD pipelines, kernel-level observability (eBPF), and scalable distributed systems.
Experience
Production AWS platform engineering for a high-concurrency ride-hailing platform. Managed multi-tenant EKS clusters, ArgoCD GitOps deployments, Terraform IaC modules, Prometheus/Grafana observability, and automated CI/CD pipelines maintaining 99.95% uptime.
Enterprise networking across multi-site infrastructure. Managed BGP/OSPF dynamic routing, Cisco switching, SD-WAN failover, IPsec VPN tunnels, and hybrid cloud connectivity with automated telemetry and incident troubleshooting.
Skills
Selected Work
All projects→Course Thesis: Autonomous real-time maritime domain awareness and anomaly detection across contested Gulf chokepoints using Go streaming pipelines, circular manifold feature engineering, and ROCm-accelerated ensemble machine learning.
Course Thesis: Design, mathematical validation, and threat modeling of an offline-first, zero-knowledge cryptographic vault deploying memory-hard Argon2id key derivation and field-level XChaCha20-Poly1305 AEAD authenticated encryption.
Course Thesis: High-throughput document transformation engine in Go designed to bridge visual 2D PDF layout representations and LLM semantic context windows via AST paragraph reflow, heuristic noise stripping, and automated chapter-segmented RAG indexing.
Writing
All articles→Research
All papers→An exhaustive empirical investigation into transitioning containerized cloud ingress and east-west service routing from conventional Linux Netfilter/iptables architectures to programmable Extended Berkeley Packet Filters (eBPF) and eXpress Data Path (XDP). The paper evaluates kernel bypass mechanisms, Maglev consistent hashing algorithms, stateful connection tracking BPF maps, and in-kernel line-rate DDoS filtering across 25GbE network fabrics.
A rigorous mathematical and architectural investigation into minimizing cross-cloud latency while enforcing zero-trust cryptographic microsegmentation across distributed on-premises and multi-cloud environments. The paper evaluates hardware TPM 2.0 node attestation, SPIFFE/SPIRE dynamic identity issuance, and socket-level eBPF packet redirection against legacy IPsec overlays and userspace sidecar proxies across 10Gbps dedicated hybrid interconnects.